Coverity Static Application Security Testing
Static application security testing for identifying software vulnerabilities.
No pricing
Dynamic application security testing for modern tech environments.
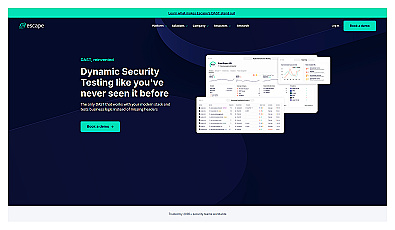
Escape focuses on dynamic application security testing, identifying security flaws in business logic that traditional methods often overlook. This product integrates well with modern technology stacks, including web frameworks and APIs.
It provides visibility into application security, allowing teams to proactively address potential risks. By streamlining security testing, Escape fits naturally into development practices, making it an essential asset for security teams. Organizations can automate API security testing and continuously monitor API exposure while reducing false positives in their security reports.
This approach helps improve compliance with security standards and supports incident response planning, ultimately enhancing the overall security posture.
Static application security testing for identifying software vulnerabilities.
AI-driven API vulnerability assessment and compliance reporting.
Automated penetration testing for security vulnerability detection.
Automated security assessments for AI systems to find vulnerabilities.
Automated reporting for pentesting to enhance security assessments.
Streamlined software development and deployment automation.